PepiteData Julien Laurenceau
  • Home
  • Services
  • Audits
  • Expert Call
  • About
  • Blog
  • Contact

security

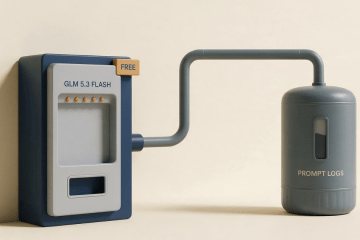
A navy vending machine labeled GLM 5.3 FLASH and FREE on a cream background, with a pipe from its back feeding a tank labeled PROMPT LOGS
AI

Your AI Supply Chain Is a Production Dependency. Audit It Like One.

Two movements meet: AI is getting production responsibilities, and production data is flowing through AI. Anthropic’s September report, malicious routers, training data provenance and model drift show what to verify before an AI reaches production.
By Julien Laurenceau, 2 months2026-09-12 ago
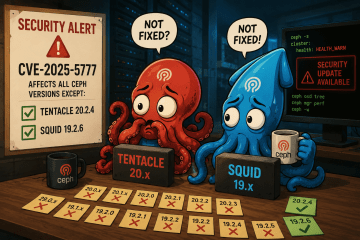
Ceph security update illustration showing Tentacle 20.2.4 and Squid 19.2.6 releases
ceph

Ceph CVEs: auth service entities with insecure key types

Ceph 20.2.4 and 19.2.6 patch four authentication and authorization CVEs. The remediation also needs CephX key rotation, client checks, and RGW multisite planning.

By Julien Laurenceau, 2 months2026-08-24 ago
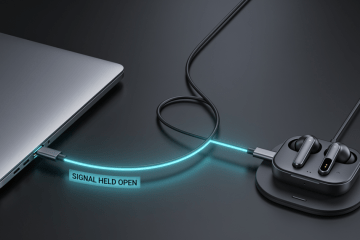
A dark laptop with a glowing cyan signal line running to a wireless headset on its charging pad, labeled SIGNAL HELD OPEN
devops

AliExpress’s Silent Audio Script Hijacked a Bluetooth Headset

AliExpress Web Audio scripts left a Bluetooth audio path open. The evidence shows a broad anti-abuse fingerprinting system, but not a unique device ID.

By Julien Laurenceau, 2 months2026-08-24 ago
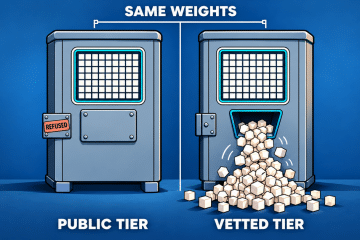
Cartoon of identical model cabinets: the public tier has a refused output, while the vetted tier releases a cascade of cubes under SAME WEIGHTS.
AI

After Coldcard: AI Security Depends on Access

The Bitcoin Red Team campaign after Coldcard exposed a dependency beyond model capability: usable access. Separate self-reported findings from confirmed vulnerabilities, then test safeguards, data controls and fallback workflows.

By Julien Laurenceau, 3 months2026-08-07 ago
  • Privacy Policy
  • Mentions légales
  • CGV
  • Cookies
Hestia | Developed by ThemeIsle